- Lockup -
- Lockup -
Lockup is a desktop security scanner and host audit platform designed for Windows systems.
Interactive GUI & Remediation
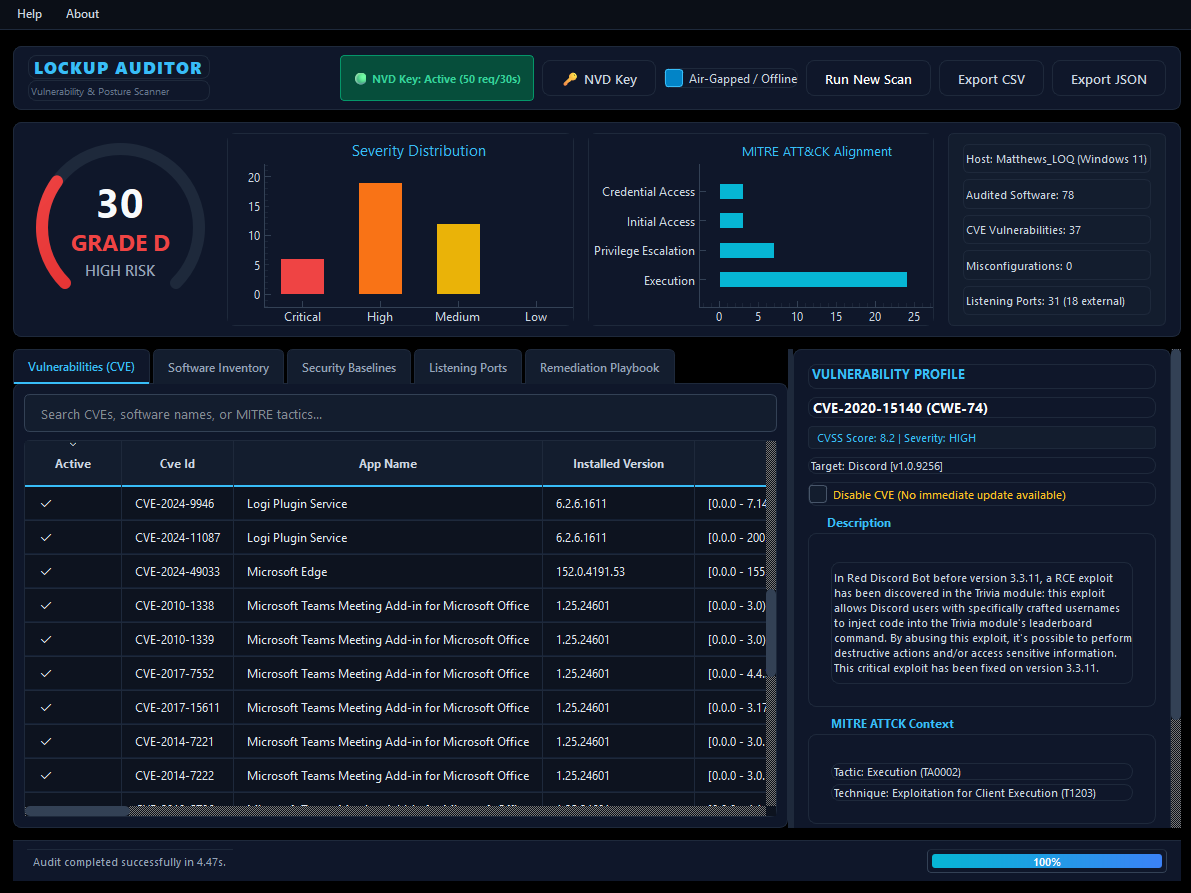
- Visual Dashboard: Interactive posture gauge, CVSS distribution charts, MITRE tactic
breakdowns, and searchable data tables.
- Automated PowerShell Playbooks: Generates actionable remediation scripts to patch
apps via winget and harden OS configuration baselines.
- Multi-Format Export: Produces executive audit reports in CSV datasets, and JSON
dumps.
Key Capabilities & Architecture
1. Host Discovery & Attack Surface Collection
- Software Inventory: Queries 32-bit/64-bit Windows Registry hives (HKLM,
HKCU, WOW6432Node) to catalog installed applications and exact versions.
- Network Exposure: Scans active TCP/UDP listening ports and correlates them to running
processes using Toolhelp32 snapshots.
- Firewall Audit: Extracts active Windows Firewall rules and inbound/outbound profiles.
Dashboard
2. OS Baseline Hardening Audit
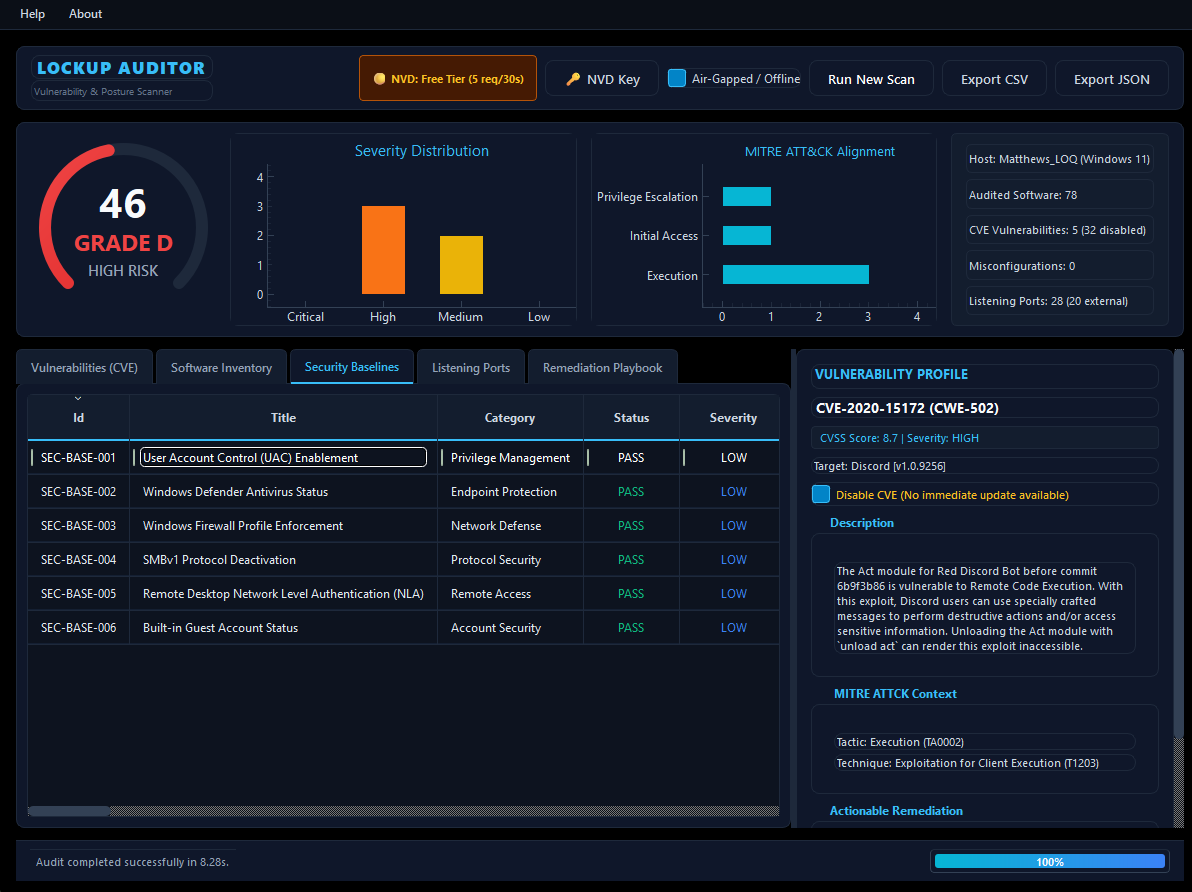
- Inspects critical Windows security settings: User Account Control (UAC), Windows Defender realtime
protection, SMBv1 protocol status, RDP Network Level Authentication (NLA), Guest Account state, and
Firewall profiles.
Baseline
3. Threat Intelligence & CVE Matching
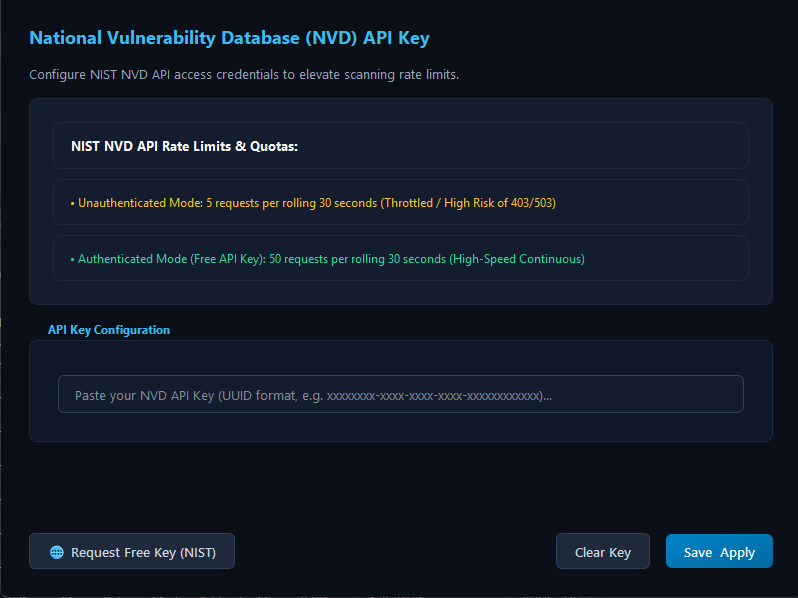
- NIST NVD 2.0 API & OSV: Fetches real-time vulnerability advisories (supports API keys
for high-throughput rate limits).
- Offline Air-Gapped Mode: Uses an embedded SQLite database for offline analysis.
- Semantic Version Matching & CPE Mapping: Normalizes product identifiers and evaluates
vulnerable version ranges.
- MITRE ATT&CK & CWE Correlation: Maps CVEs to specific ATT&CK tactics, techniques, and
weakness categories.
API-Key
4. Risk Analytics & Posture Scoring
- Aggregates vulnerability metrics using NumPy and Pandas to compute an overall Security Posture Score
(0 - 100), letter grades (A+ to F), CVSS severity distributions, and attack surface risk indices.
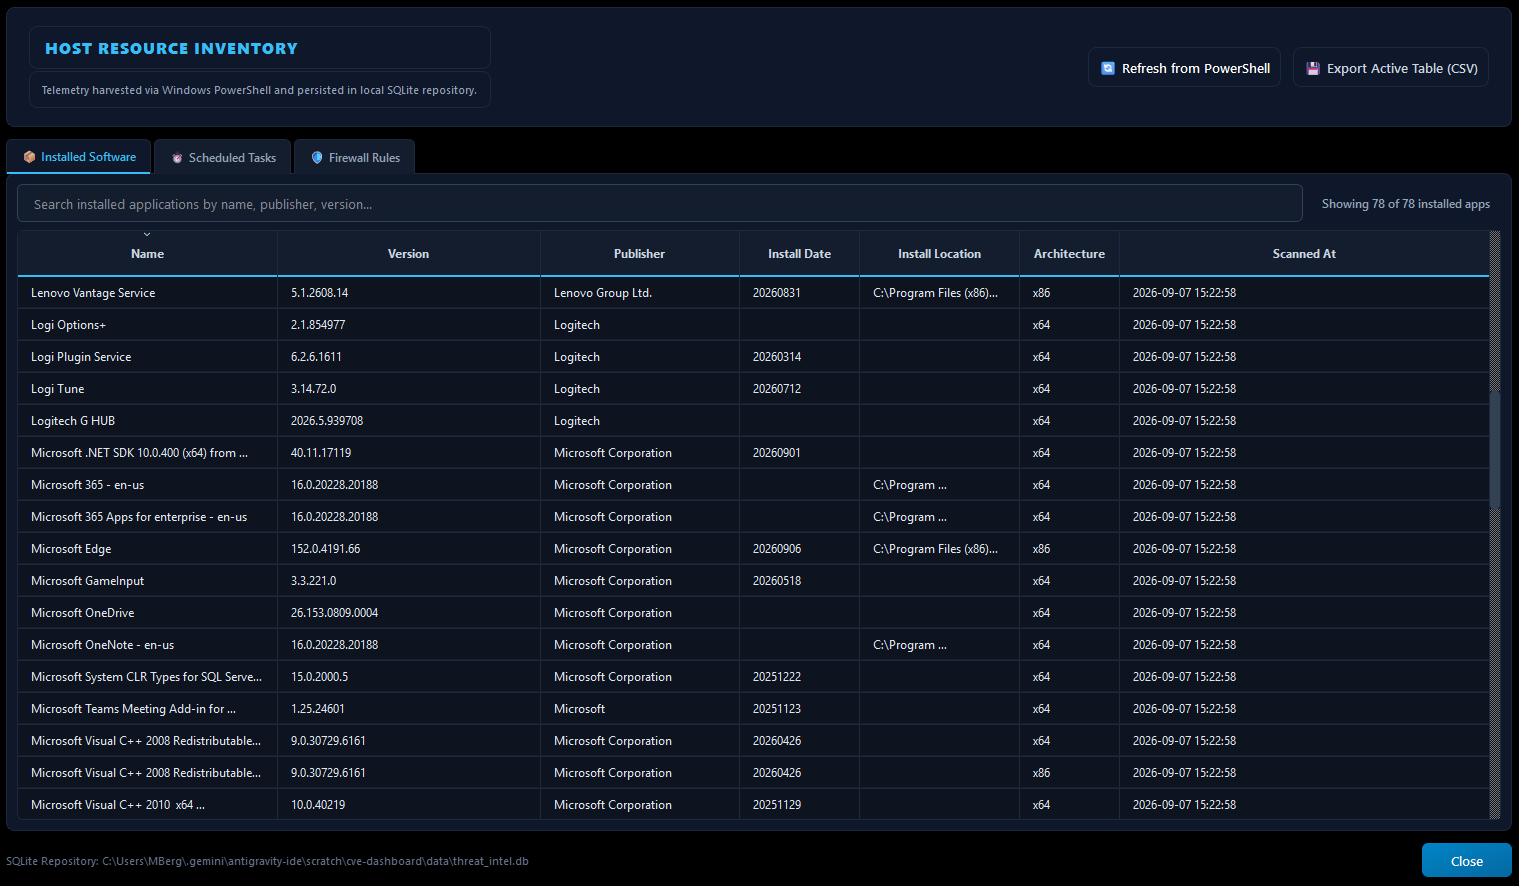
Resource Inventories
- Collects and catalogs software, scheduled tasks, and firewall rules.
- Exportable in CSV Format
Resource Inventories
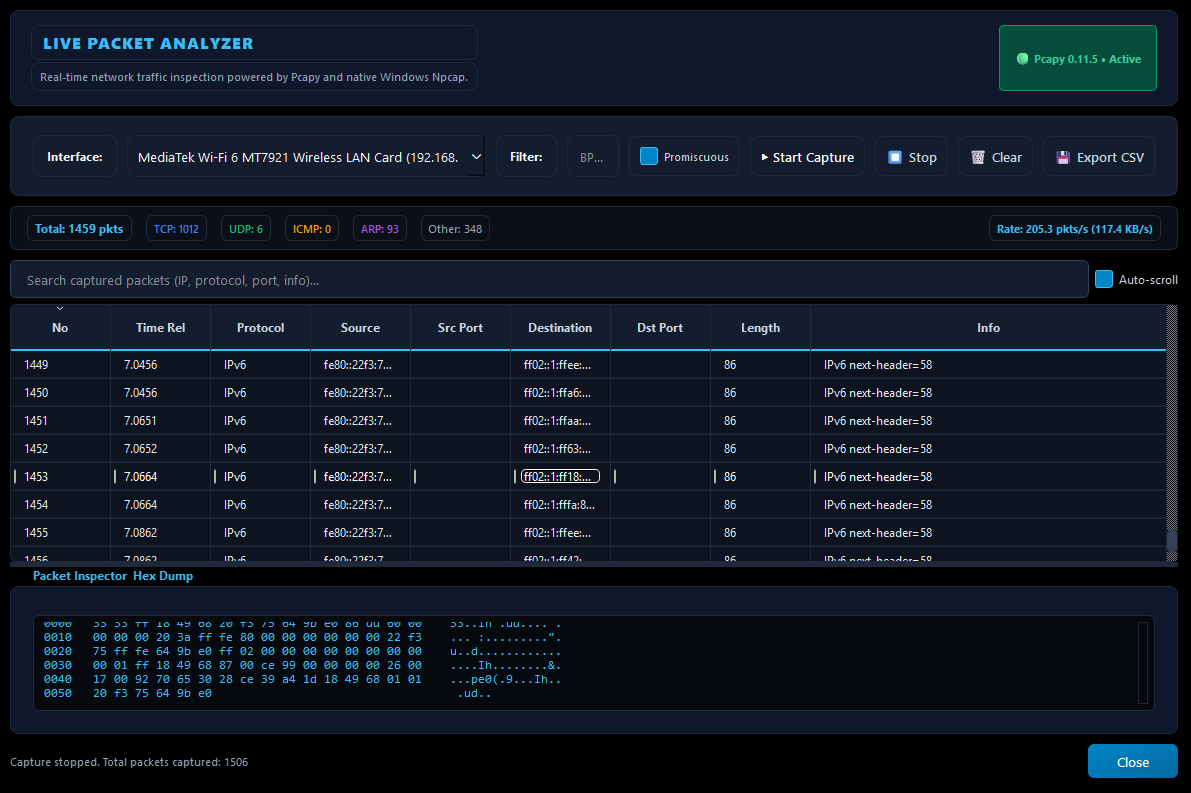
pycapy Network Monitoring
- Collects and catalogs network connections, listening ports, and associated processes.
- Micro-Sized packet capture and analysis of network traffic.
- Exportable in CSV Format.
pcapy Network Monitoring
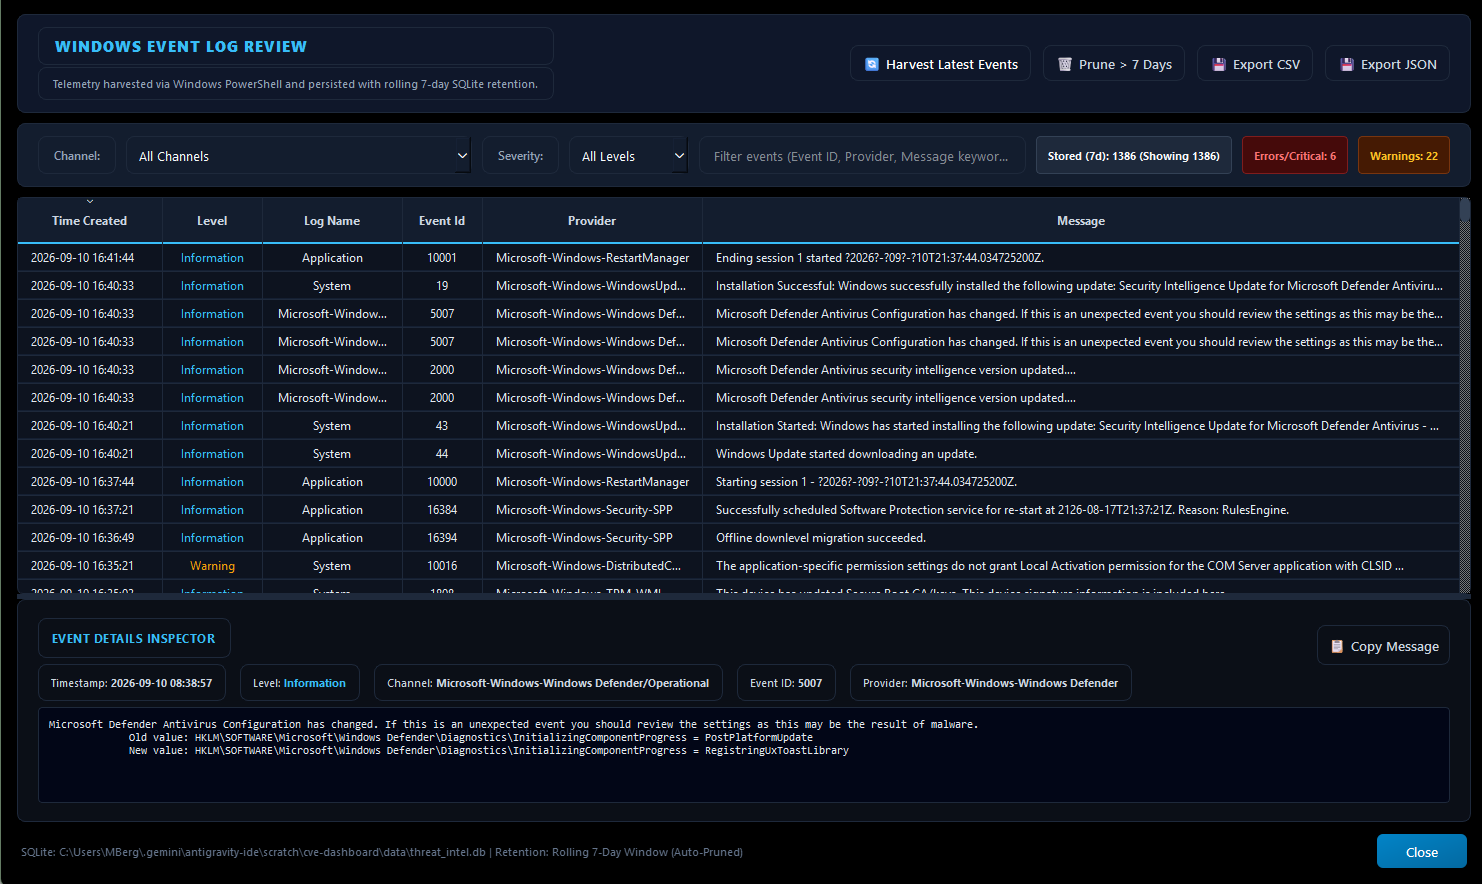
Windows Event Log Monitoring
- Collects and catalogs the last 7 days of Windows Event Logs, including Security, System, and Application logs.
- Exportable in CSV and JSON Format.
Event Log Monitoring
This tool was created for educational purposes, and can not be used towards security posturing, and to do so is at your own risk. LockUp Auditor is intended strictly for security education, research, and lab analysis. It must not be used as an authoritative basis for enterprise compliance, regulatory validation, or commercial vulnerability management without independent verification.